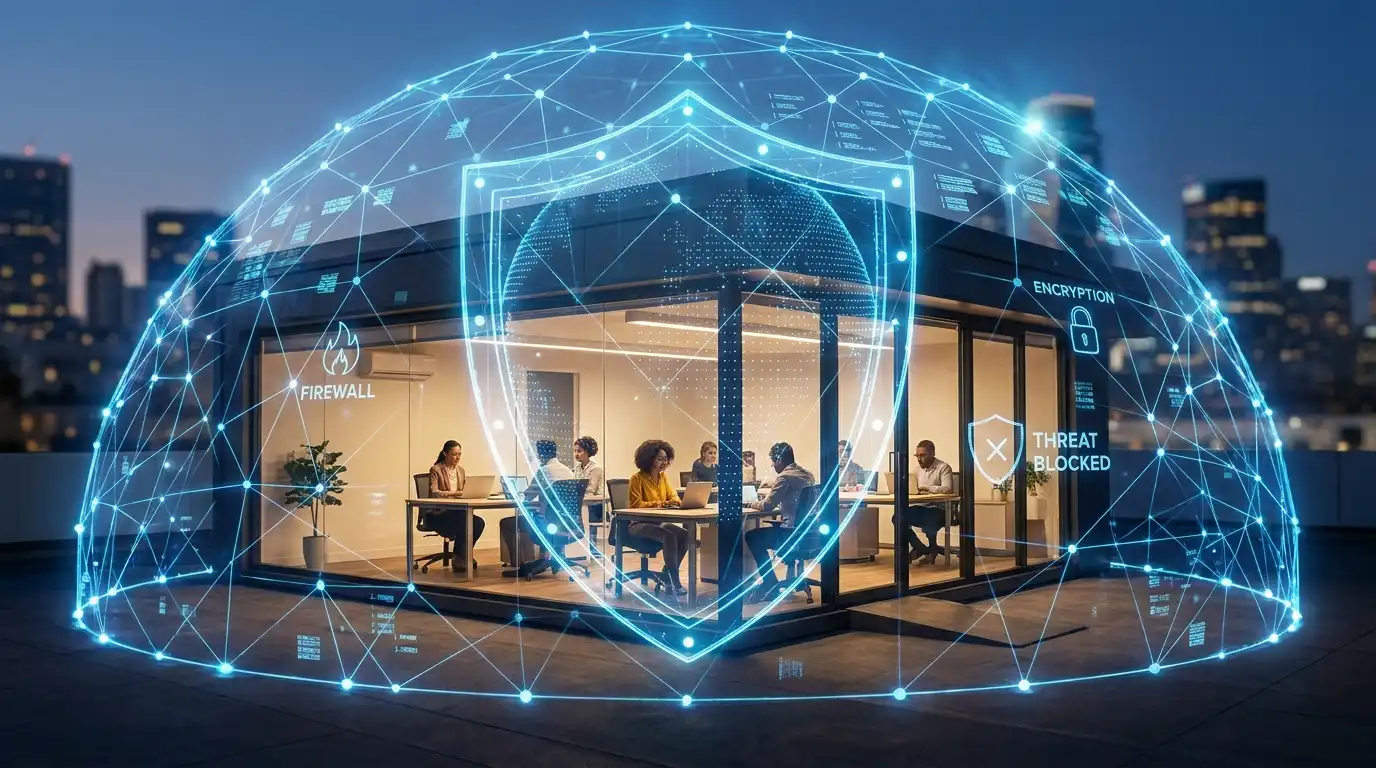
For years, small and mid-sized business owners operated under a comforting delusion: “We are too small for hackers to care about us.” While major corporations like tech conglomerates, international retail chains, and credit bureaus made national headlines when hit by massive data breaches, small businesses quietly assumed their limited digital footprints made them invisible targets.
In 2026, that assumption is not just outdated—it is dangerous. Automated hacking scripts, AI-driven phishing tactics, and widespread supply chain vulnerabilities have democratized cybercrime. Bad actors no longer spend months breaching a single fortune 500 company when they can launch thousands of automated attacks per hour against unprotected small businesses. Today, a single compromised email account, leaked customer database, or ransomware lock can shutter a small business permanently.
Traditional insurance policies offer virtually no defense against digital threats. To navigate the current risk environment, understanding and securing dedicated cyber liability insurance for small business operations is no longer optional; it is a fundamental pillar of corporate risk management.
The Evolving Threat Landscape for Small Businesses
Cybercriminals target small businesses for a very simple reason: efficiency. While enterprise organizations deploy multi-million-dollar cybersecurity departments and dedicated security operations centers, small businesses frequently rely on outsourced IT providers, basic antivirus software, and employee vigilance. Attackers view small-to-midsize businesses (SMBs) as soft targets with valuable data assets.
In recent years, the nature of these attacks has shifted dramatically:
- Ransomware as a Service (RaaS): Cybercriminals sell pre-packaged malware kits, making it remarkably easy for low-level hackers to lock your company’s operational files, customer databases, and accounting software until a steep ransom is paid.
- Business Email Compromise (BEC): Using sophisticated social engineering, bad actors spoof or hijack executive email addresses to trick employees, vendors, or clients into transferring funds into fraudulent bank accounts.
- Third-Party Vendor Exploits: Modern businesses rely on cloud software, digital payment processors, and online inventory management tools. If a software vendor you use suffers a breach, your customer records and business continuity are compromised instantly.
When an attack strikes, the immediate cost goes far beyond replacing corrupted hardware or buying new software. The real financial devastation lies in business interruption, regulatory penalties, forensic investigations, and legal liability.
First-Party vs. Third-Party Cyber Liability Coverage
A common misconception among business owners is that all cyber insurance policies operate identically. In reality, comprehensive cyber insurance policies are structured into two distinct coverage categories: First-Party Coverage and Third-Party Coverage.
1. First-Party Cyber Coverage (Direct Operational Costs)
 First-party coverage protects your business against the direct, immediate costs resulting from a cyber incident. When your systems are compromised, this coverage kicks in to cover:
- Forensic Investigations: Hiring specialized cybersecurity experts to identify the breach source, contain the intrusion, and verify that hackers are fully removed from your network.
- Business Interruption Losses: Replacing lost income, ongoing payroll obligations, and operating costs while your systems are offline or functioning at reduced capacity.
- Data Recovery & Restoration: Rebuilding damaged databases, restoring lost files, and repairing corrupted operating systems.
- Extortion & Ransomware Costs: Negotiating with threat actors and paying digital ransom demands when no alternative recovery path exists.
- Crisis Communications & PR: Retaining public relations professionals to preserve your brand’s reputation and handle client communications transparently.
2. Third-Party Cyber Coverage (Legal & Regulatory Claims)
If customer financial details, medical records, or sensitive corporate data are exposed during a breach, affected clients, partners, and government agencies may pursue legal action against your company. Third-party coverage protects you from claims that your business failed to maintain adequate data security standards. It typically covers:
- Legal Defense Expenses: Retaining specialized privacy attorneys to represent your company in court.
- Settlements & Judgments: Covering court-ordered compensation, client settlements, or class-action lawsuit outcomes.
- Regulatory Fines & Penalties: Navigating compliance investigations under state data privacy laws or federal frameworks like FTC Privacy and Security Guidelines.
- Customer Notification & Credit Monitoring Services: Mandatory costs associated with notifying every impacted individual and providing them with complimentary credit monitoring services for 12 to 24 months.
Why General Liability Policies Leave You Completely Exposed
One of the most dangerous gaps in small business risk management is the belief that standard commercial property or commercial general liability (CGL) policies cover cyber incidents. They almost certainly do not.
Standard Commercial General Liability policies were designed for physical injury and physical property damage—such as a customer slipping on a wet floor or an employee accidentally damaging a client’s vehicle. CGL policies explicitly contain digital data exclusions. In the eyes of an insurance carrier, digital data, customer lists, and software code are intangible assets, not physical property.
Similarly, standard commercial property insurance covers physical perils like fire, theft of physical equipment, or water damage. If a laptop is physically stolen from your office, commercial property coverage may pay $1,500 to replace the hardware. However, it will cover $0 of the $250,000 in liability incurred because the unencrypted customer database stored on that laptop was exposed.
Qualifying for Coverage: Security Controls Insurers Require
Due to the sharp rise in cyber claims globally, insurance carriers have become highly selective. Securing a cyber liability policy in 2026 requires more than simply filling out a one-page form and paying a premium. Insurers expect applicants to demonstrate basic digital hygiene before issuing a policy.
To qualify for affordable cyber liability coverage, your business should implement the following baseline security controls:
- Multi-Factor Authentication (MFA): Mandating MFA across all corporate email accounts, remote desktop protocols (RDP), cloud storage platforms, and administrative access points.
- Immutable Cloud Backups: Maintaining secure, encrypted data backups that are stored offsite and completely disconnected from the primary network to prevent ransomware from encrypting backups alongside live files.
- Endpoint Detection & Response (EDR): Utilizing modern EDR software across all company desktops, laptops, and servers instead of relying on legacy signature-based antivirus software.
- Patch Management & Employee Training: Enforcing strict protocols for software updates and conducting regular phishing simulations to train employees on identifying suspicious emails.
Protecting Your Business’s Digital Future
A cyberattack is no longer a rare, worst-case scenario reserved for sci-fi scripts or giant corporations; it is a routine operational risk that every modern business owner must address. For a small business, a severe data breach or prolonged ransomware outage can easily trigger six-figure losses—an unexpected expense that forces many unmanaged companies into bankruptcy.
Cyber liability insurance acts as a vital financial backstop, ensuring that a single malicious email link or software vulnerability does not undo years of hard work. By auditing your current digital exposure, implementing essential security controls, and securing a dedicated cyber insurance policy, you safeguard not only your business assets, but your reputation and peace of mind.